WarBrief Live | November 9, 2026 | Cybersecurity
996
switches compromised
48
countries hit
10
GS1900 models affected
8.8 / 9.8
CVSS score (Zyxel / Binarly)
CVE-2026-107441 is an unauthenticated out-of-bounds write in Zyxel GS1900 switches that lets attackers run commands as root — and it survived the June patch meant to stop the attacks. Zyxel’s fix, firmware V2.90 Patch 3, is available now.
Key Takeaways
- Attackers compromised 996 Zyxel GS1900 switches across 48 countries from around August 17, 2026, stealing device configurations, hashed root credentials and network information, according to GreyNoise.
- The attacks were first blamed on CVE-2026-7273, patched in June — but Binarly proved the exploit targeted a separate, unpatched flaw, CVE-2026-107441, that worked on every June-patched firmware.
- Ten GS1900 models running firmware 2.90 Patch 2 or earlier are affected. The fix is V2.90 Patch 3, released on October 22, with Zyxel’s advisory published on November 3.
- Patching alone is not enough: 564 of the 996 compromised switches still used factory-default credentials, so owners must also rotate credentials and check for signs of compromise.
What is CVE-2026-107441?
CVE-2026-107441 is an out-of-bounds write vulnerability — tracked as CWE-787 — in the dispatcher.cgi program that handles the web management interface of Zyxel’s GS1900 series smart managed switches. An attacker who can reach that interface can send a crafted HTTP request that writes data beyond the memory buffer the software was given, corrupting adjacent memory and hijacking the device’s execution flow. The result, as Binarly’s advisory BRLY-2026-057 puts it, is that an unauthenticated remote attacker can execute arbitrary operating-system commands with root privileges. No username or password is needed.
The flaw affects ten GS1900 models — the GS1900-8, 8HP, 10HP, 16, 24, 24E, 24EP, 24HPv2, 48 and 48HPv2 — running firmware 2.90 Patch 2 or earlier. Zyxel and the US National Vulnerability Database score the flaw 8.8 out of 10 under CVSS 3.1, with an adjacent-network attack vector, while Binarly rates it 9.8, treating it as remotely exploitable over the network. The disagreement matters: Zyxel’s score assumes the attacker must already be on the local network, while Binarly’s assumes the management interface is reachable — which, in practice, it often is, because many small networks never segment it.
These are not exotic devices. GS1900 switches are the quiet boxes that connect computers, printers and servers inside small offices, schools, clinics and homes. A compromised switch sits in the middle of the network, able to observe traffic and serve as a foothold for deeper intrusion. That is why a flaw in a humble switch drew the attention of a state-linked campaign — and why the patch history matters as much as the flaw itself.
Why didn’t the June patch stop the attacks?
On June 16, 2026, Zyxel released firmware updates addressing CVE-2026-7273, a pre-authentication buffer overflow in the same GS1900 switches, and published its advisory for that flaw. Administrators who installed the update — firmware 2.90 Patch 2 — had every reason to believe the window had closed. It had not.
From around August 17, cybersecurity company GreyNoise observed a suspected Chinese-speaking threat actor it tracks as Kapibala exploiting GS1900 switches, reporting that the attackers compromised 996 devices across 48 countries. When GreyNoise published its report, “Open Season on Kapibala”, on September 21, it attributed the exploitation to CVE-2026-7273 — the flaw Zyxel had patched in June. That same day, the US Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-7273 to its Known Exploited Vulnerabilities catalogue, requiring federal agencies to address it.
The attribution was wrong. Researchers at firmware security firm Binarly, investigating infrastructure linked to the JITTERLY backdoor and the SIXZUT rootkit, found an exposed archive containing an obfuscated Python exploit targeting Zyxel GS1900 switches. Analysing it, they discovered something striking: the exploit specifically checked whether the target firmware had already been patched for CVE-2026-7273 — a sign it had been developed or updated to work on patched devices. Binarly confirmed on September 28 that the exploit remained effective against all ten firmware releases patched for the June flaw.
The root cause, as Binarly’s technical analysis explains, is a copy-before-check error. The CGI parser stores request parameters in a global object with 140 entries of 1,024 bytes each, followed by a counter. The code copies data into memory before validating the counter, so an oversized value can corrupt it; a negative counter then lets the attacker write memory before the buffer and hijack function pointers. Zyxel’s June fix had added a count check — but the unsafe copy still ran first, so the check came too late. Binarly reported its findings to Zyxel on September 29. Zyxel confirmed the new vulnerability on October 11 and assigned it CVE-2026-107441, treating it as a separate flaw because the exploit also abused missing validation of HTTP parameter lengths. The June patch had fixed a real bug. It had simply not fixed the bug the attackers were using.
How the Zyxel zero-day unfolded: June to November 2026
- June 16, 2026: Zyxel releases firmware 2.90 Patch 2 fixing CVE-2026-7273, a pre-authentication buffer overflow in GS1900 switches, and publishes its advisory.
- August 17, 2026 (around): GreyNoise observes the Kapibala actor exploiting GS1900 switches. The campaign ultimately compromises 996 devices across 48 countries, stealing configurations, hashed root credentials and network information.
- September 21, 2026: GreyNoise publishes “Open Season on Kapibala”, attributing the exploitation to CVE-2026-7273. CISA adds CVE-2026-7273 to its Known Exploited Vulnerabilities catalogue the same day.
- September 28, 2026: Binarly confirms the recovered exploit still works against all ten firmware releases patched for CVE-2026-7273.
- September 29, 2026: Binarly reports the separate vulnerability to Zyxel.
- October 11, 2026: Zyxel confirms the new flaw and reserves CVE-2026-107441.
- October 22, 2026: Zyxel releases V2.90 Patch 3 firmware, which limits parameter sizes and validates the parameter count before copying data into memory.
- November 3, 2026: Zyxel publishes its advisory for CVE-2026-107441; Binarly publishes its advisory BRLY-2026-057 and its technical analysis the same day.
- November 4, 2026: Canada’s Centre for Cyber Security updates alert AV26-1114, noting that open-source reporting indicates the flaw is being exploited in the wild.
One date deserves emphasis: the attacks began in mid-August, but the real flaw was not publicly identified until November 3. For nearly three months, defenders who had patched in June believed they were protected while the exploit kept working. As BleepingComputer reported, it remains unclear whether the exploit was deliberately developed to bypass the June updates or simply exploited a related weakness the earlier patches failed to address. Either way, the lesson is the same: a patch only protects against the flaw it actually fixes, and confirming that requires testing the exploit against patched firmware — which is exactly what Binarly did.
By the numbers: what is confirmed and what is only reported
| Metric | Figure | Source |
|---|---|---|
| Switches compromised | 996 | GreyNoise (reported, not confirmed by Zyxel) |
| Countries affected | 48 | GreyNoise (reported) |
| Most affected countries | Italy 133, United States 129, Taiwan 123, France 90, South Korea 69 | GreyNoise (reported) |
| Compromised switches still on factory-default credentials | 564 of 996 (57%) | GreyNoise (reported) |
| GS1900 models affected | 10 | Zyxel advisory (confirmed) |
| CVSS 3.1 score | 8.8 (Zyxel, NVD) / 9.8 (Binarly) | Zyxel / Binarly (confirmed, scoring differs) |
| Advisory published | November 3, 2026 | Zyxel (confirmed) |
| Fixed firmware | V2.90 Patch 3 (.3C0 builds) | Zyxel (confirmed) |
| CISA KEV listing for CVE-2026-107441 | Not listed as of November 5, 2026 | CISA catalogue (confirmed) |
Caveat: the 996-switch figure comes from GreyNoise and Binarly reporting; Zyxel has not confirmed it, and its own advisory does not claim the flaw was exploited. The available evidence also does not establish that all 996 switches were compromised after Patch 2 was installed — some may have been hit through factory-default credentials or unpatched firmware. What is established is that exploitation happened, and that the attack path survived the June fix.
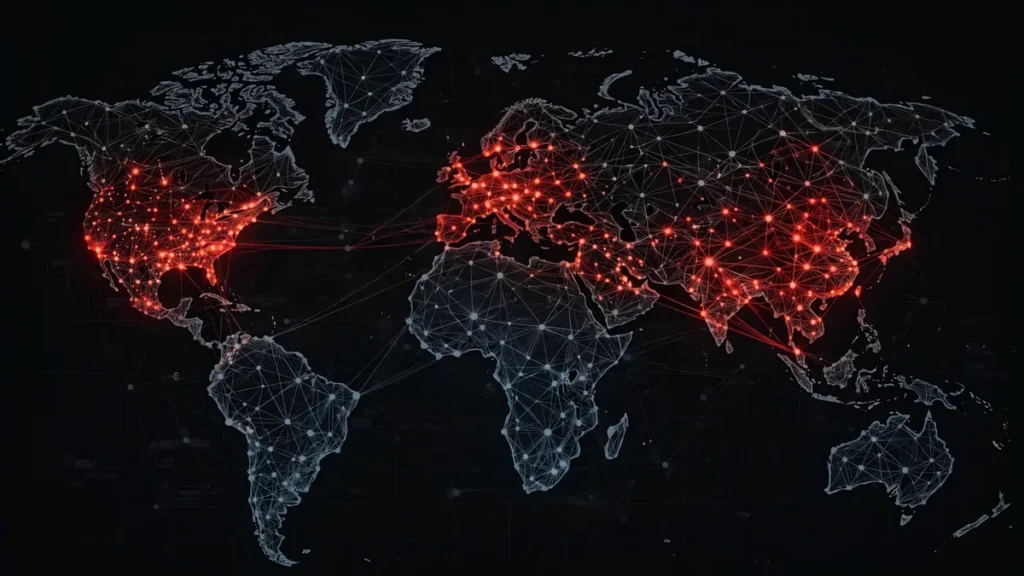
Who is behind the attacks — and why attribution is contested
GreyNoise tracks the actor as Kapibala and describes it as a suspected Chinese-speaking threat actor, linking it to the Red Heron campaign — a cluster previously reported by Acronis as exploiting a critical vulnerability in the self-hosted Git service Gitea. The same campaign, GreyNoise reported, also compromised WordPress sites, stealing more than 18,000 sensitive records from a Western government organisation. The Zyxel switches were one strand of a broader espionage-style operation, not an isolated incident.
Attribution is not settled. Sekoia’s Threat Detection and Research team, which spotted the operation in mid-October 2026, assessed with moderate to high confidence that the activity is linked to APT29 — also known as Midnight Blizzard or Cozy Bear, and tied to Russia’s SVR foreign intelligence service. That assessment points in a different direction from GreyNoise’s Red Heron linkage. No government has publicly attributed the activity, and the two assessments rest on different evidence: GreyNoise on shared infrastructure and tooling, Sekoia on its own telemetry. Until more evidence is published, the honest description is that the actor is tracked as Kapibala, that researchers disagree on its sponsorship, and that the victim data — not the attribution — is the part administrators can act on.
What is not in dispute is the mechanism. The exploit was recovered from infrastructure associated with the JITTERLY backdoor and the SIXZUT rootkit, and Binarly’s analysis of it is public. That transparency is what allowed the misattribution to CVE-2026-7273 to be corrected at all — and it is a reminder that in incident response, the first diagnosis is not always the right one.
What the Zyxel zero-day means for US/UK/EU readers
If you run a small business, a school, a clinic or a home office with a Zyxel GS1900 switch, this story is directly about your network. The affected models are common in exactly those settings, and the most affected countries in GreyNoise’s data include the United States (129 compromised switches), France (90) and Italy (133) — this was not a campaign confined to one region.
First, check your firmware. If your switch runs 2.90 Patch 2 or earlier, install V2.90 Patch 3 — the “.3C0” build for your model — from Zyxel’s support site. Zyxel’s Patch 3 release note lists the fixed build for each of the ten models. Do not assume the June update covered you: that is precisely the mistake this campaign exploited.
Second, rotate your credentials. Patching closes the hole; it does not undo stolen data. GreyNoise found that 564 of the 996 compromised switches still used factory-default credentials — and even switches that were patched may have had their root credential hashes exfiltrated before the fix. Change the admin password, and if the switch was ever reachable from the internet, treat its configuration as compromised and review it.
Third, segment the management interface. The flaw needs network access to the switch’s web management page. If that page is reachable from the wider network — or from the internet — the risk is far higher than if it is restricted to a management VLAN. Restricting access is the single cheapest mitigation, and it is good practice regardless of this flaw. Finally, look for signs of compromise: unexpected configuration changes, unfamiliar admin accounts, or outbound connections to unknown hosts are all worth investigating before you declare the device clean.
What to watch next in the Zyxel GS1900 patch fallout
The immediate question is whether CISA adds CVE-2026-107441 to its Known Exploited Vulnerabilities catalogue. As of November 5 it had not — only the older CVE-2026-7273 is listed — which means federal agencies are not yet formally required to remediate the real flaw. A KEV listing would force the issue and, just as importantly, correct the record for organisations that closed their tickets in June.
The second question is whether Patch 3 holds. Binarly’s researchers have shown a willingness to test Zyxel’s fixes against the recovered exploit, and the pattern of this story — a patch that looked complete but was not — argues for independent verification rather than trust. Watch for follow-up analysis from Binarly and for any further Zyxel advisory. Zyxel published a separate advisory in the same window for CVE-2026-76955, a buffer overflow in certain access points and security routers, which suggests the vendor’s review of its web-facing code is still turning up issues.
The third question is disclosure: whether Zyxel, or any affected organisation, publishes victim numbers of its own. Until then, the 996 figure remains researcher-reported, and the true scale — including switches compromised quietly and never counted — is unknown. For now, the actionable facts are clear: ten models, one real fix, and a June patch that never did what everyone thought it did.
Read next: WarBrief’s Ivanti zero-day chain explainer covers another case where a patched flaw was not the flaw being exploited, and our 3AM ransomware explainer looks at how attackers are using AI-assisted intrusions against UK schools. For the broader picture, see the WarBrief intelligence hub and our conflict zones coverage, plus the Palo Alto GlobalProtect flaw that ransomware gangs exploited earlier this year.
Frequently asked questions
What is CVE-2026-107441?
CVE-2026-107441 is an out-of-bounds write vulnerability in the web management interface of Zyxel GS1900 switches. It lets an unauthenticated attacker who can reach the interface run operating-system commands with root privileges through a crafted HTTP request, with no login required.
Which Zyxel switches are affected by CVE-2026-107441?
Ten GS1900 models are affected: the GS1900-8, 8HP, 10HP, 16, 24, 24E, 24EP, 24HPv2, 48 and 48HPv2, running firmware 2.90 Patch 2 or earlier. The fix is V2.90 Patch 3, released on October 22, 2026.
Why didn’t the June 2026 Zyxel patch stop the attacks?
The June patch fixed a different flaw, CVE-2026-7273. Binarly discovered that the exploit used in the attacks targeted a separate, unpatched vulnerability — CVE-2026-107441 — and that it worked on every firmware version carrying the June fix, because the June fix added a validation check after the unsafe data copy had already run.
How many Zyxel switches were compromised?
GreyNoise reported that 996 GS1900 switches across 48 countries were compromised, with configurations, hashed root credentials and network information stolen. The figure comes from researcher reporting and has not been confirmed by Zyxel, and 564 of the 996 switches still used factory-default credentials.
What should I do if I own a Zyxel GS1900 switch?
Install V2.90 Patch 3 for your model, change the admin password and rotate any credentials that may have been exposed, restrict the management interface to a trusted segmented network, and check the switch for unexpected configuration changes or unfamiliar accounts.
Sources
- BleepingComputer: Zyxel fixes zero-day exploited to hack nearly 1,000 network switches
- Binarly: Out-of-bounds write vulnerability in Zyxel GS1900 switches allows unauthenticated remote code execution (BRLY-2026-057)
- GreyNoise: Open Season on Kapibala — Attacker Steals Over 18,000 Government Records Through WordPress Exploitation
- Zyxel Community: Switch GS1900 Series — V2.90 Patch 3 Firmware Release
- eSecurity Planet: Zyxel GS1900 Zero-Day — Why June’s Patch Failed
- Cyber Daily: Patch now — Zyxel patches switches left vulnerable since June
Discussion 0
Share analysis, corrections, or context. Be civil — comments are moderated.